Content Security Policy
The two CSP directives Pulse needs, and how to add them without weakening your policy.
If your site sends a Content-Security-Policy header, the browser blocks anything the policy
doesn't explicitly allow — including Pulse. Two hosts need to be allowed, one per job:
script-src https://js.ciphera.net; connect-src https://pulse-api.ciphera.netMerge these into your existing directives — don't replace your policy. If your policy already
has a script-src or connect-src list, append the host to it. If it has neither, the browser
falls back to default-src, so add the hosts there instead.
What each directive is for
script-src https://js.ciphera.net— where the tracking script itself is served from. Without it the script never loads, and Pulse never runs.connect-src https://pulse-api.ciphera.net— where the script sends events. Without it the script loads and runs, but every event is blocked in the browser — the dashboard stays empty while the install looks fine in your HTML.
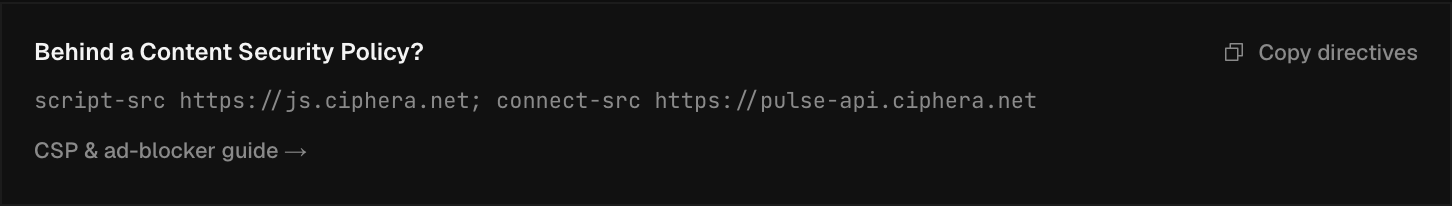
The setup panel in Pulse (Settings → Site → General, under "Behind a Content Security Policy?") carries this exact pair with a copy button.
Nonce- and hash-based policies
If your script-src uses nonces ('nonce-…', often with 'strict-dynamic'), allowing the host
alone is not enough — the browser also requires the nonce on the tag. Add your page's nonce
attribute to the Pulse <script> tag the same way you do for your own scripts:
<script src="https://js.ciphera.net/…" nonce="YOUR_PAGE_NONCE" defer></script>With 'strict-dynamic', keep https://js.ciphera.net in the list anyway — browsers that don't
support 'strict-dynamic' fall back to the host allowlist.
If your script-src allows hashes instead of hosts (script-src 'sha384-…'), turn on
Subresource Integrity (SRI) in the same setup panel instead of adding the nonce. It swaps the
script tag for a version-pinned URL with a matching integrity="sha384-…" attribute, and browsers
check that attribute against the hash-source values in script-src, so the tag can pass a
hash-only policy without a host in the allowlist. Copy the same hash the toggle put in the tag into
your script-src list; adopting a new script version means updating both.
How a CSP problem looks
Open your browser's developer console on your own site. A blocked install shows one of:
Refused to load the script 'https://js.ciphera.net/…' because it violates … script-src …
Refused to connect to 'https://pulse-api.ciphera.net/…' because it violates … connect-src …
The first means the script never ran; the second means it ran but its events are blocked. In both cases the install panel in Pulse keeps "Listening for your first event…" — the server never saw anything. Once the directive is deployed, events confirm within seconds of a page load.
No console errors but still no data? That's usually not CSP — an ad blocker or tracking-protection extension can drop the same requests without printing anything. Test in a browser profile without extensions, then see Troubleshooting for the rest of what to check.